Systems | Development | Analytics | API | Testing

WSO2 Optimizes Developer Experience with Launch of WSO2 Identity Server 7.0

WSO2 Identity Server 7.0 expands developer productivity with a new authentication API, visual editor with side-by-side graphical and code views, and one-click templates and authentication methods; adds comprehensive B2B CIAM and financial-grade API security.
Introducing Identity Server 7.0 - The Most Powerful and Developer-Friendly Release Yet

WSO2 Identity Server is the leading open source IAM solution. It is a powerful, modern access management solution for your on-premises or cloud environment that provides secure access for your consumers (B2C), enterprise customers (B2B), workforce (B2E), or APIs. WSO2 Identity Server manages more than 1 billion identities worldwide, and its extensibility allows it to support the most complex IAM requirements.

Automating ETL Tasks Effectively with Choreo

Connecting multiple systems and exchanging data among them is afrequent requirement in many business scenarios. This typically involves one or many source systems, an intermediary processor, and one or many destination systems. Some organizations invest in purpose-built solution suites such as Data Warehouse, Master Data Management (MDM), or Extract, Transform, Load (ETL) platforms, which, in-theory, cover a wider spectrum of requirements.

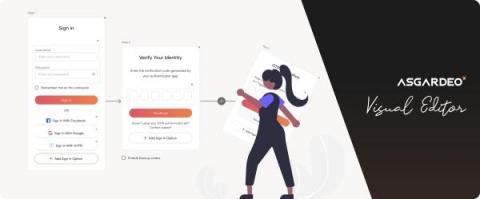
Simplify Application Login Flows with Asgardeo's New Visual Editor

App developers seeking simple login integration often find the IAM landscape daunting. Easier said than done when app developers don't live and breath the intricacies of identity standards. With Asgardeo, we have bridged this gap and offer a smooth experience for developers trying to ship their apps as soon as possible. In this post, let's dig into the newly delivered Login Flow Visual Editor and learn about the thinking behind this new capability and what it has to offer.

WSO2 API Manager: Leading the Way in API Management and Security

API management and API security are like two sides of a coin, intrinsically part of a greater whole. That is why the recent KuppingerCole report, “Leadership Compass: API Security and Management,” is particularly useful for organizations seeking to develop or update their API strategies. With the report’s comprehensive view of both API management and security, it offers an invaluable resource for understanding their interplay.

Streamlining Cloud Native App Development in Kubernetes with Prioritized API Management

For years, we've witnessed how applications have shifted to the cloud, driven by cost savings, flexibility, on-demand access, scalability, and faster deployment times. During that time, new architectural best practices for building cloud native applications have emerged. (For more insights, refer to this whitepaper.) Yet despite these advances, it remains difficult to build cloud native applications that fully take advantage of Kubernetes, the platform of choice for most cloud deployments.

The Illusion of Control: Why In-House Platforms Can Undermine Your Business Strategy

In the rapidly evolving tech landscape, the promise of control reigns supreme. And, it’s why founders, CEOs, and technical decision-makers are increasingly drawn to the idea of building in-house platforms. The appeal is understandable: complete sovereignty over every layer of the tech stack, from the user interface down to the most granular data interactions. It's an intoxicating vision that promises a bespoke solution tailored precisely to a company's unique needs.

Pushing the Boundaries of OAuth and OIDC Security - Push Authorization Request (PAR)

In the world of API security, OAuth 2.0 plays a crucial role in authorization. OpenID Connect (OIDC) works seamlessly with OAuth 2.0, providing an identity layer that ensures standardized authentication and user information for applications. Among various grant types, the Authorization Code stands out as a recommended standard. It's known for its advanced security features, support for refresh tokens, reduced exposure of credentials, and adaptability for both server-side and front-end applications.